Webinar
Agent Runtimes on Kubernetes: Isolation, HA, and OpenShell vs. Agent Substrate
Tuesday October 20 @9am PT / 12pm ET
Running an AI agent in a sandbox is one thing. Running isolated, highly available agents in production is another.
NVIDIA OpenShell and similar approaches focus on secure agent execution, while Agent Substrate provides the infrastructure layer for running stateful agents on Kubernetes. This session compares the approaches, including what true workload isolation means beyond simply putting agents in containers, and what it takes to make an agent runtime genuinely highly available.
See how kagent builds on Agent Substrate to deliver a production agent runtime with durable state, multi-zone workers, stateless service replicas, and recovery from node and zone failures, alongside agentgateway for secure agent-to-tool connectivity.
You'll learn:
- How true sandbox isolation differs from simply running agents in containers
- How Agent Substrate compares with approaches such as OpenShell
- What high availability for stateful agents actually requires, including durable state, multi-zone workers, replicas, and failure recovery
- How kagent builds on Agent Substrate to manage and govern agents in production
- How agentgateway provides connectivity, security, and policy for agent-to-tool traffic
- How to test HA in practice with node kills, zone failures, and rolling restarts
Register now
Register now
Agent Runtimes on Kubernetes: Isolation, HA, and OpenShell vs. Agent Substrate
Agent Runtimes on Kubernetes: Isolation, HA, and OpenShell vs. Agent Substrate
Webinar
Thanks for registering!
A confirmation will be sent to your email.

Speakers
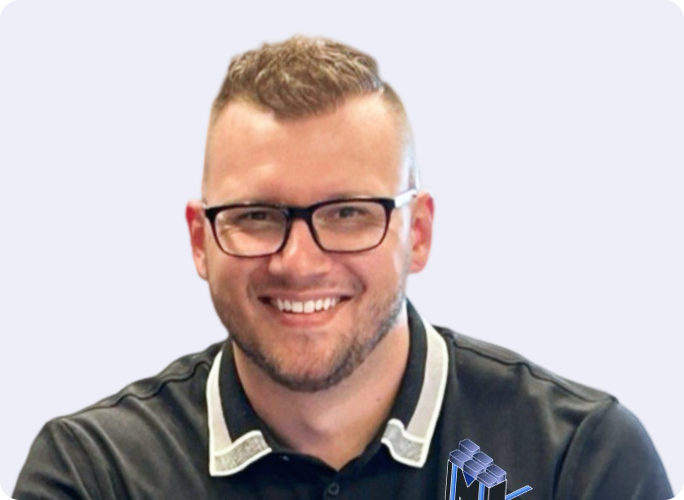
Michael Levan
AI Architect
Focusing on providing business value through technology, working directly with customers, providing first-class advisory, and content, Michael Levan helps organizations address needs through Agentic AI practices. He has worked across industries as an engineer, consultant, trainer, and content creator. He's a CNCF Ambassador, AAIF Ambassador, 4x published author, international speaker, and was part of the Kubernetes v1.28 and v1.31 Release Teams. Michael's approach translates technical complexity into business value, delivering actionable solutions that enhance performance, security, observability, and agentic workloads.